Launch your AI-built app without getting hacked
$10
Problem:
You built your own app. It works, it looks great, and you're ready to ship. But here's the uncomfortable question: is it actually secure? If an AI tool wrote some or all of your code, it doesn't reliably catch its own security mistakes, and nobody else is reviewing it for you. Examples are exposed API keys, wide open database rules, missing rate limits, etc. You don't know what you don't know, and one miss can turn your launch into a disaster.
Solution:
I spent 3.5 years as a software engineer inside the cybersecurity division of a Fortune 500 fintech company. I built an app the division used to report on 700,000+ apps and assets against the company's security standards, and my own app had to pass the same scans. As a new engineer I got flagged for the same mistakes I see in apps today, so I know how easy they are to make and how hard they are to spot when nobody has shown you. I've taken what those scans actually check and rewritten it in plain English for apps you built yourself. I walk you through each check step by step and explain every term as it comes up, so you can find the problems before an attacker does.
What you get:
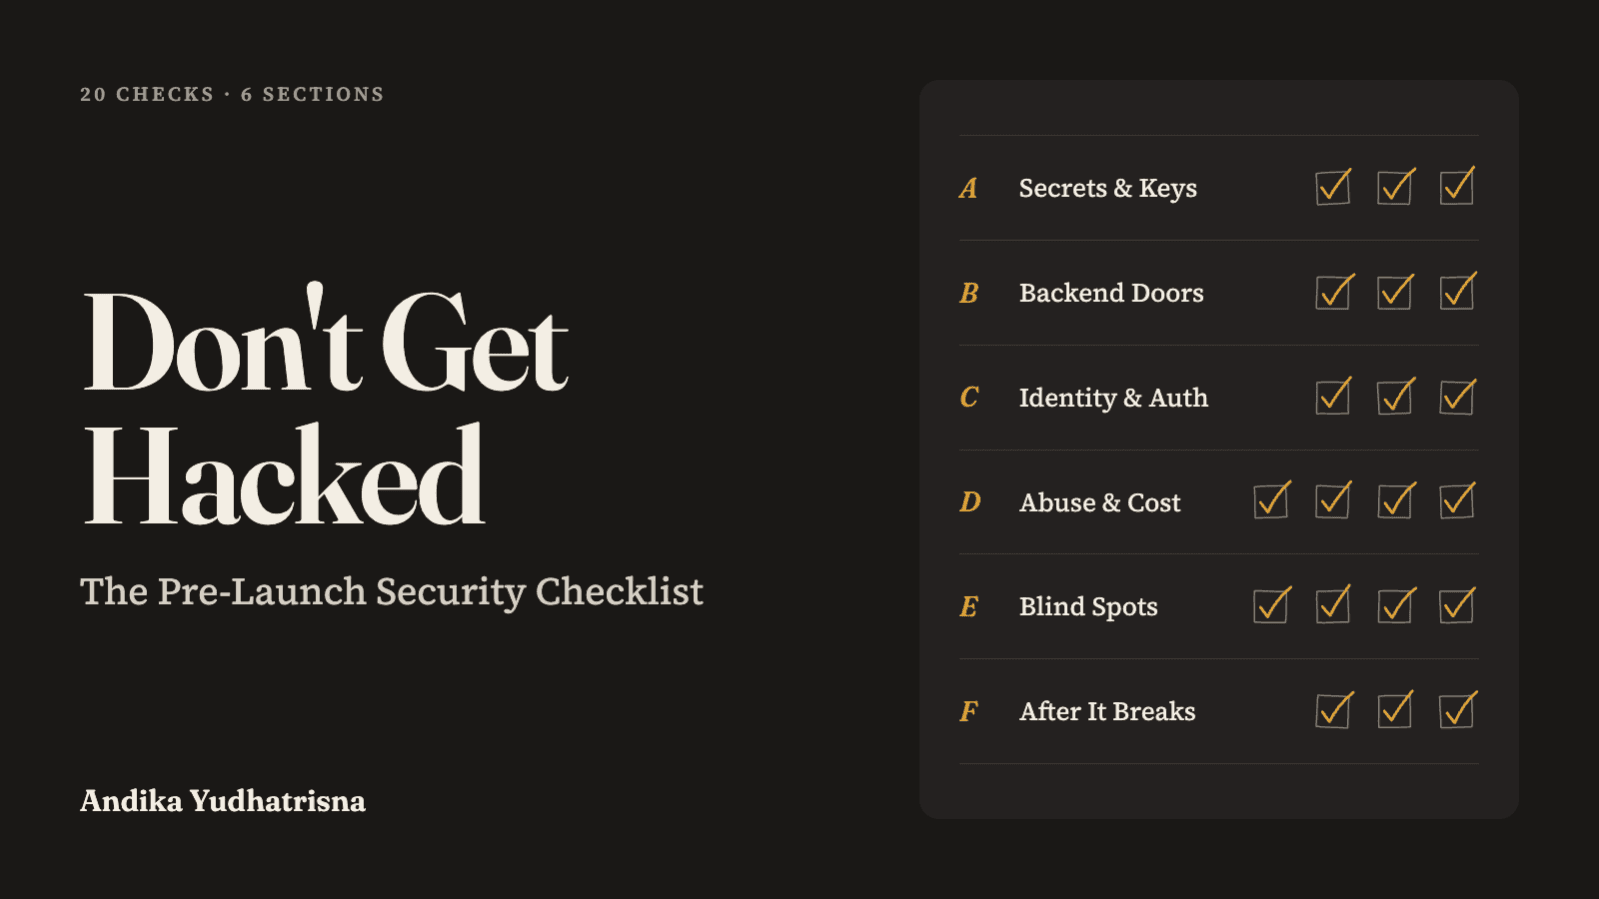
20 checks across 6 sections: each one ends with a clear pass line, so you know whether you passed or failed.
Step-by-step "how to verify it": written for someone with no security background, with every term explained the first time it appears.
"If you failed" fixes: what to do for each way a check can go wrong.
15 copy-paste AI prompts: use your own assistant to help run the checks on your code.
A tick-box checklist of all 20 checks: each line links back to its full check, so you can re-run it after every big change.
What it covers:
Secrets & Keys: no key in your code, your git history, or the browser.
Backend Doors: database rules, and who can read whose data.
Identity & Auth: login, tokens, and MFA on the accounts that control your app.
Abuse & Cost: a firewall, rate limits, and spending ceilings, so a bot can't run up your bill.
Blind Spots: dependencies, leaky error pages, encryption, and payments.
After It Breaks: error alerts, backups, and a restore you've actually tested.
The guarantee:
You get the full guide right after purchase. If you're not happy with it, email me within 7 days for a full refund, no questions asked.